InferLabs — Security engineering, Australia

Machines write the code.
Now they hold the keys.

Every control that matters now sits downstream of something that is not a person. We build for that spot in the stack — a vault an agent cannot read its way out of, and an assessment platform that treats evidence as the output rather than the paperwork.

01 — Position

An agent runs as you.

It reads every credential you can read and touches every repository you can touch, at a rate no review process was built to absorb. That is not an argument for stopping. It is an argument for moving the control.

We spent fifteen years running security inside organisations that could not afford to be wrong — Amazon, Cisco, Macquarie, NAB, and Australian government programs. The lesson repeated itself every time: the control that works is the one standing in the execution path, not the one written in the policy document. Everything else is a record of what you intended.

So we build in the path. Take the secret off the disk and put a broker where it used to be. Make the assessment emit its own evidence rather than a separate reporting exercise. Small, checkable mechanisms — the kind you can read the source of in an afternoon and decide for yourself.
02 — Products

Two tools, one seam.

01

Akasha

A local vault for AI agents.

Open source · Alpha

An agent inherits your credentials the moment you start it. Akasha takes the secrets off the disk and puts a broker in front of them, so an agent uses a key one operation at a time and nothing is written to disk. Every use is recorded against a token rather than the value, and nothing leaves the machine.

Go daemon · MCP · Apache 2.0

02

Granular

Assessments that produce their own evidence.

For assessment teams

Essential Eight, ISM, IRAP. The assessment is real work; the spreadsheet archaeology around it is not. Granular runs the pipeline from kickoff to signed report, so the deliverable falls out of doing the work instead of becoming a second project after it.

Control libraries · Evidence tracking · Reporting

Currently shipping

A credential that never lands on disk.

Akasha is the piece of this we care most about, and the piece you can check yourself. It is open source, it is pre-1.0, and it says so on the tin.

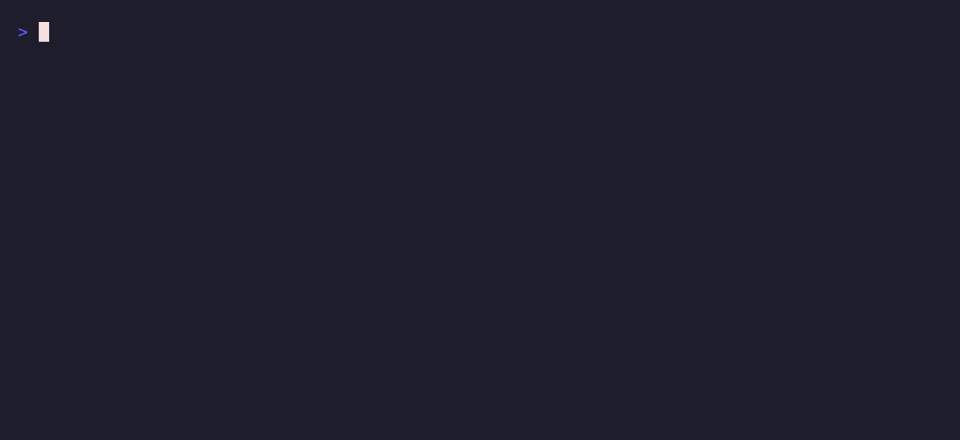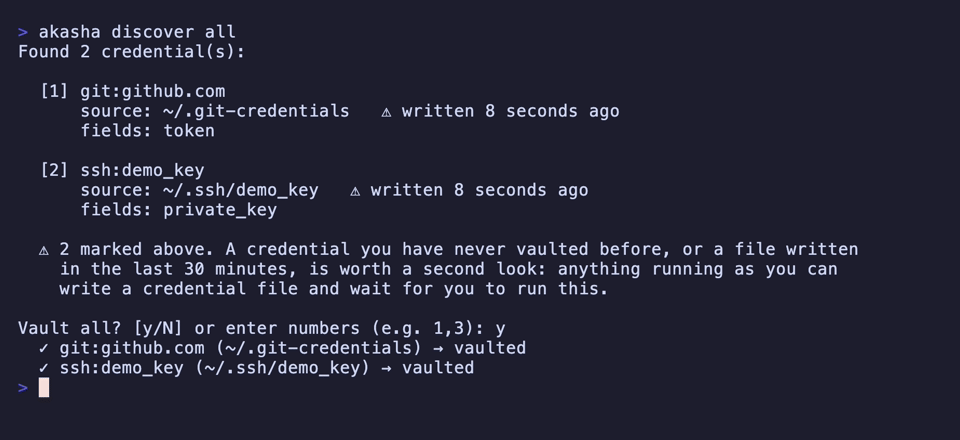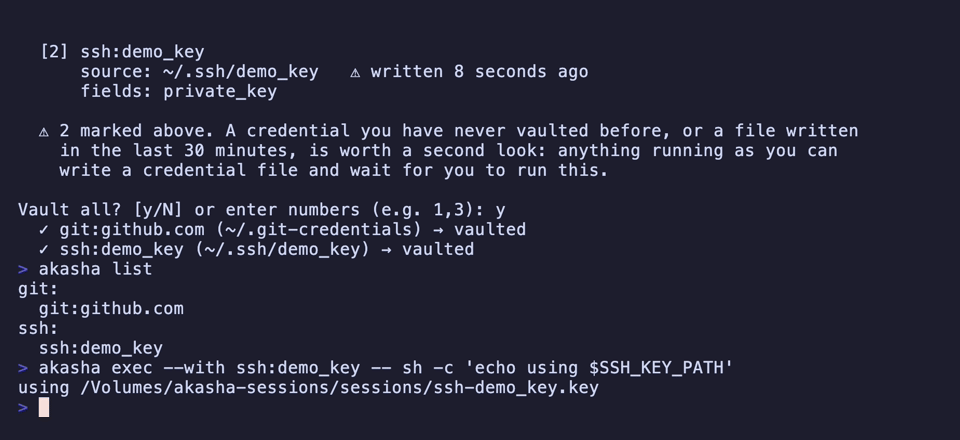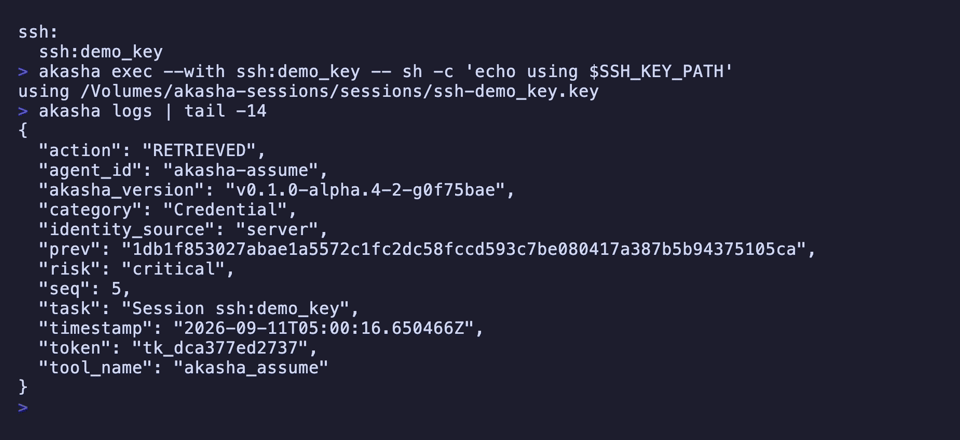
Terminal recording: Akasha finds credentials in plaintext, vaults them on confirmation, then runs a command using one it never exposes — recording the access against a token digest rather than the secret.
Real output, recorded against synthetic credentials in a throwaway environment.

Possession, not interception

A secret that exists only in the vault has no plaintext left to steal. Bypassing the interception layers gains nothing, because there is nothing on disk to read.

One operation at a time

The broker returns the bytes for that operation and writes nothing to disk. Policy runs per operation: allow, deny, or ask — and ask fails closed.

Providers are data

Integrations are signed YAML selecting from a fixed set of primitives. No command field, no shell, no expression language — so there is no slot to inject one.

$ curl -sSL https://getakasha.dev/install | sh
$ akasha setup

  Scanning for credentials…
 AWS default profile   → vaulted
 SSH key id_ed25519    → vaulted

03 — Who is behind it

Where we have done this before

Security and platform engineering at Amazon, Cisco, Macquarie and NAB, and across Australian government programs — the assessing side as often as the assessed side.

What we are fluent in

Essential Eight, the ISM, and IRAP assessment — including the evidence standard each of them actually holds you to, which is rarely the one in the summary.

How we build

Local-first by default. Open source where the trust argument depends on being readable. No telemetry to disable, because there is none to begin with.

Tell us what you are trying to protect.